Snort deployed in the dmz network, Computer Networking

Assignment Help:

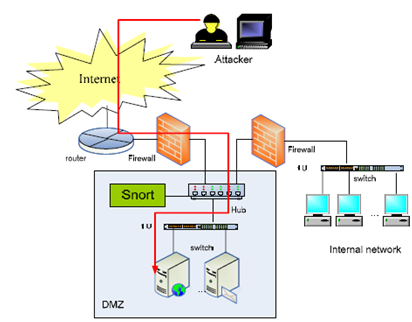
Let's consider the network shown in Figure 1 where Snort is deployed.

In Figure 1, why is Snort deployed in the DMZ instead of the Internal Network?

In Figure 1, say True or False to the following statement: "Snort can see both incoming packets from the left firewall and outgoing packets from the right firewall".

In Figure 1, assume a packet P matches the following Snort rule when the packet is analyzed by Snort.
1336_Compute the hash - part of the packet.png

Is packet P a TCP packet or a UDP packet?

Is packet P an incoming packet or an outgoing packet?

What is the source IP address contained in the header of packet P?

What is the destination IP address contained in the header of packet P?

Who is the receiver program of this packet?

The payload of packet P must contain four specific bytes. What are the four specific bytes?

Since packet P matches the rule, an alert will be raised and the Security Administrator will receive a notice (message) from Snort. What will the notice say to the administrator?

A Phf attack is a remote to local (R2L) attack against the Web Server running the "Phf" CGI script. Phf script has vulnerability that, when exploited, allows remote users to execute arbitrary commands on the Web Server and such commands will be written as:
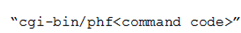
368_Snort deployed in the DMZ Network.png


Attackers can launch this attack from any PC connected to the Internet, and the target system can be any apache web servers that permit access to the Phf script. Let's assume that the Web Server shown in Figure 1 (inside DMZ) is an apache web server that permits Phf scripts and let's assume the IP address of the Web Server is 195.4.12.5. Please give a concrete Snort rule that can detect Phf attacks against the Web Server.

To be able to detect attack packets, Snort firstly needs to log the corresponding traffic. For this purpose, the Snort administrator will need to set up several log rules. Please give a log rule to let Snort log UDP traffic from any IP address with any port going to computers on the Internal Network specified with a Class C IP range 195.4.13.0/24.

Explain the meaning of the following Snort rule.
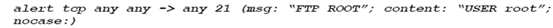
1217_Snort deployed in the DMZ Network1.png


Related Discussions:- Snort deployed in the dmz network

Network analyzers, NETWORK ANALYZERS: A network analyzer also known ne...

NETWORK ANALYZERS: A network analyzer also known network monitor or a network sniffer is used to calculate the performance of or debug a network. It may report statistics s

What is network architecture, What is Network Architecture? When two o...

What is Network Architecture? When two or more computer are linked with one another for the purpose of communicating data electronically, besides physical connection of comput

Dns message - application layer, DNS Message There are  the only  two ...

DNS Message There are  the only  two kinds  of DNS message DNS query and reply messages. Further mote both query  and reply message have  the same  format  as shown in figure.

Subtract two from number of hosts, Why do we require to subtract two from n...

Why do we require to subtract two from number of hosts?

Write a descriptive note on rmonv2, Question 1 What does the SNMP access p...

Question 1 What does the SNMP access policy represent? Question 2 Does there exist any formal functional specification for SNMPv1 management? Question 3 In the con

Explain the types of security service, Q. Explain the Types of Security Ser...

Q. Explain the Types of Security Service? Security Services fall into one of the subsequent categories - Confidentiality: Confirms that the info in a system and transm

Wireless access - computer network, Wireless Access Wireless access co...

Wireless Access Wireless access connecting end  systems ( that are often  mobile) into the network. Today there are two broad types  of wireless internet access(1) wireless an

Combine subtitution and transposition, how to own cipher to encrypt and dec...

how to own cipher to encrypt and decrypt message by combine both substitution ans transposition algorithm using c program

Transport layer , Transport Layer In computer networking it the transp...

Transport Layer In computer networking it the transport  layer is where  sessions are  exchanged between  hosts. This layer resides  between  the application layer and  networ

Write Your Message!

Captcha
Free Assignment Quote

Assured A++ Grade

Get guaranteed satisfaction & time on delivery in every assignment order you paid with us! We ensure premium quality solution document along with free turntin report!

All rights reserved! Copyrights ©2019-2020 ExpertsMind IT Educational Pvt Ltd